CompTIA Security+ Certification Milestone
Overview
I am excited to share that I successfully passed the CompTIA Security+ certification exam with a score of 782.
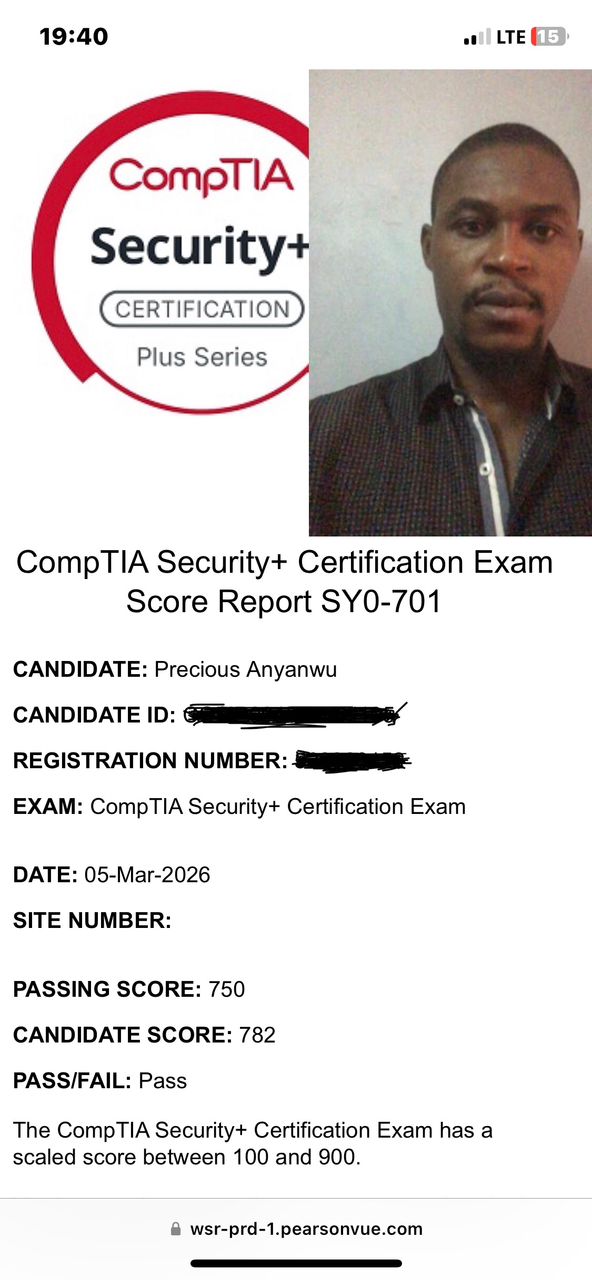
Security+ is a globally recognized cybersecurity certification that validates foundational knowledge across:
Threat detection and response
Network security
Identity and access management
Security architecture
Cryptography and PKI
Security operations and incident response
This milestone represents a significant step in my journey toward becoming a Security Operations Center (SOC) Analyst.
My Cybersecurity Learning Journey
My preparation for Security+ built upon several years of structured learning and hands-on practice in cybersecurity, networking, and cloud security.
Prior to this certification, I obtained the ISC2 Certified in Cybersecurity, which provided a strong introduction to core security principles.
To reinforce theoretical knowledge, I focused heavily on practical labs and investigation-based learning, documenting my work throughout the process.
Some of the practical areas I worked on include:
Malware traffic analysis using packet captures
Network packet investigation with Wireshark
Log analysis using tcpdump
Threat intelligence lookups using VirusTotal
Identifying Indicators of Compromise (IOCs)
Network scanning and anomaly detection
These hands-on exercises helped translate certification concepts into real-world security investigation workflows.
Study Strategy
My Security+ preparation combined conceptual study, hands-on labs, and exam simulations.
Study Resources
Key learning resources included:
Official CompTIA Security+ study materials
Practice exams and scenario-based questions
Security investigation labs using PCAP files
Network protocol analysis exercises
I also simulated multiple exam-style scenarios to strengthen my understanding of:
Security controls
Authentication mechanisms
Network attack detection
Risk management strategies
Skills Developed During Preparation
Preparing for Security+ strengthened my understanding of several important cybersecurity domains:
Network Security
Secure protocols and port usage
Network segmentation and firewall concepts
Intrusion detection principles
Threat Detection
Identifying suspicious network behavior
Recognizing command-and-control traffic
Investigating malware indicators
Identity and Access Management
Authentication protocols (RADIUS, SAML, LDAP, Kerberos)
Multi-factor authentication mechanisms
Cryptography
Hashing vs encryption
TLS security mechanisms
Certificate validation and PKI
Practical Security Projects
During my preparation I completed and documented several investigation labs, including:
Malware Traffic Analysis using Wireshark
Qakbot Malware PCAP Investigation
Network Log Analysis with tcpdump
These projects are available in my GitHub portfolio and demonstrate practical SOC-style analysis workflows.
Next Steps
With Security+ completed, my focus is now on expanding practical security monitoring and cloud security skills.
Planned projects include:
Building a Snort IDS detection lab
Implementing a SIEM log monitoring environment
Developing cloud security monitoring labs in AWS
I am also currently preparing for the AWS Certified Solutions Architect – Associate exam.
Conclusion
Passing Security+ marks an important milestone in my cybersecurity journey. My focus going forward is to continue developing hands-on experience in security monitoring, incident detection, and cloud security architecture.
I am actively building projects and labs that simulate real-world SOC environments and security investigations.
If you are interested in cybersecurity investigations, threat analysis, or cloud security, feel free to explore the other projects in my portfolio.
Repository Purpose
This post documents a key milestone in my cybersecurity learning journey and reflects my commitment to continuous learning and practical skill development.