Observing Plaintext HTTP Traffic Using Packet Capture
🌐 Project Overview
This lab demonstrates how HTTP traffic is transmitted in plaintext and can be observed using packet capture tools. The objective was to show why unencrypted protocols like HTTP present security risks, as sensitive data can be exposed during transmission.
📄 Full Technical Report:
Download the Plaintext HTTP Traffic Analysis Report
🧪 Lab Setup
| Role | Tool Used |
|---|---|
| Packet Capture | tcpdump |
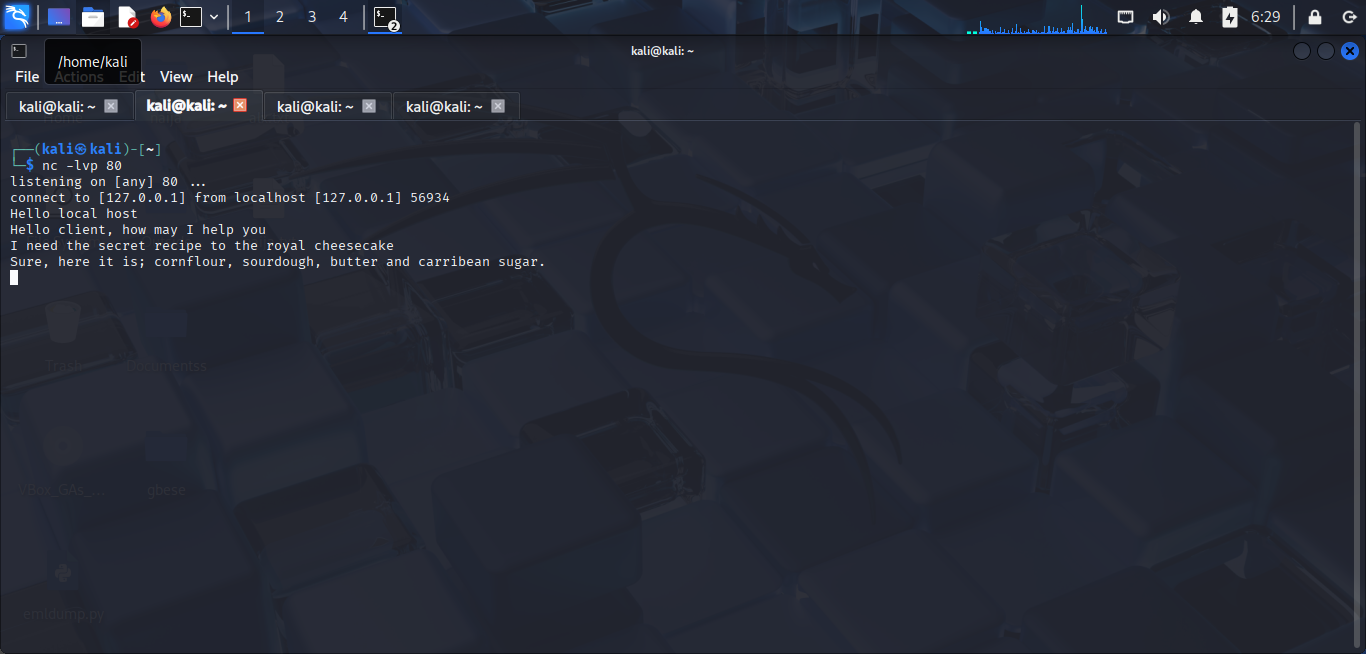
| Server | Netcat (nc) listening on port 80 |
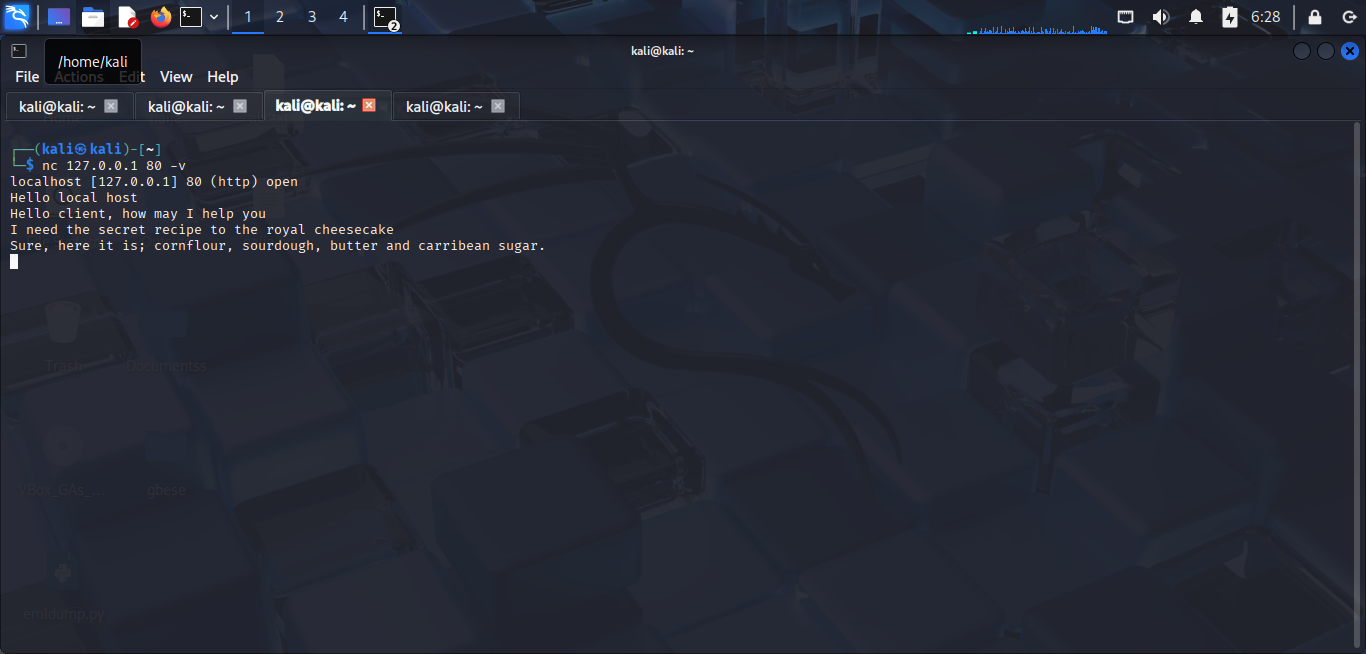
| Client | Netcat (nc) connecting to localhost |
| Interface | Loopback (lo) |
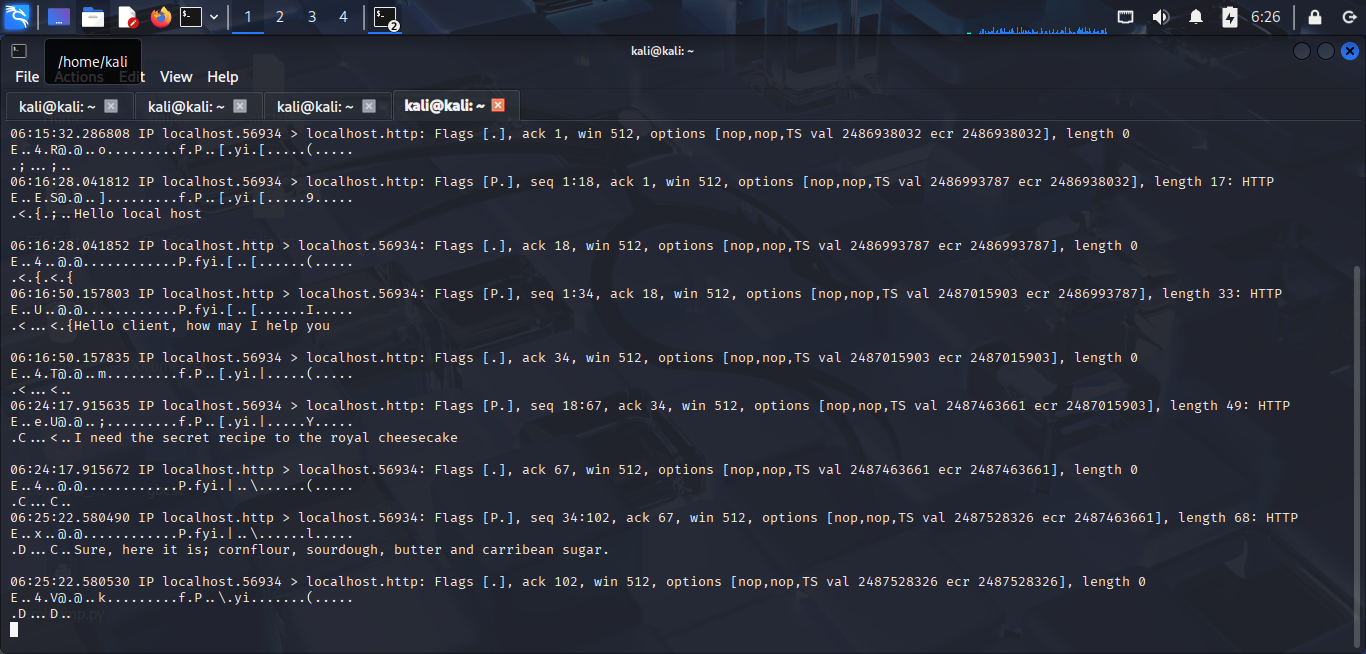
⚙️ Packet Capture
```bash sudo tcpdump -i lo -A
Server Configuration
nc -lvp 80
Client Connection
nc 127.0.0.1 80 -v
🔍 Key Observation The captured packets revealed that HTTP traffic is readable in plaintext. Data appeared in ASCII format within tcpdump output, demonstrating the absence of encryption.
🔐 Security Implication
Unencrypted HTTP traffic allows attackers on the network to intercept and read transmitted data. This highlights the importance of HTTPS and TLS encryption.
.
🎯 Skills Demonstrated
Packet capture and inspection
Understanding of plaintext vs encrypted traffic
Security implications of unencrypted protocols
Practical traffic monitoring